Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

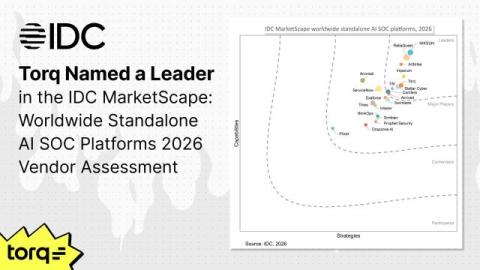
Torq Named a Leader in IDC MarketScape: Worldwide Standalone AI SOC Platforms 2026 Vendor Assessment

Chris Kissel, Vice President of IDC Security & Trust, just drew a line in the sand for the AI SOC category with one simple sentence: “Vendors that can show their agents reason transparently, act within defined guardrails, and improve with each investigation will define this category. The rest will be measured against them.” We couldn’t agree more.
A DR plan isn't proven until you test it

The quick answer: A disaster recovery (DR) plan is only a hypothesis until it’s tested under real conditions. Regular, scoped DR and cyber recovery testing, covering people, dependencies, data, and systems, exposes the gaps that a written plan can’t reveal. 11:11 Systems helps IT and business continuity leaders validate recovery readiness before a real incident forces the issue. Think of a DR plan like a fire escape map taped to the back of a hotel room door.

Inside the HulkApps Shopify Checkout Hijack

Shopify phishing has evolved from the laughable “Dear Shopify Merchant” email into one of the most reliable account-takeover vectors in ecommerce. On the same pattern, Shopify shops have recently been hit with a checkout hijack campaign running through HulkApps, Swym, and Selleasy extensions, where shoppers on legitimate stores were redirected to a fake payment page on biliingtop that captured their card details before forwarding them to the real Shopify checkout.

Federal Breaches Continue: Why Identity and Access Management Matters Now More Than Ever

Federal agencies are facing a critical reckoning with cybersecurity. In the past year alone, high-profile breaches have exposed millions of Americans’ personal data, compromised sensitive intelligence networks and revealed significant gaps in access control practices across some of the government’s most trusted institutions.

LimaCharlie Code Security marks a fix verified only when production runs it

Co-founder and CCO Most code scanners stop at a merged pull request. LimaCharlie Code Security keeps going until the fix is running. Code Security is now generally available in the LimaCharlie Cloud Security extension. It scans GitHub, GitLab.com, and Bitbucket Cloud repositories, ranks code findings next to your cloud risk, and checks every fix against what your workloads actually run. Most code security tools declare victory at merge.

Stop Guessing. Find the Root Cause with Cato DEM.

When a user says, “the application is slow,” IT has to answer a much harder question: where did the problem actually begin? The issue could be on the endpoint, local network, ISP, the network path, enterprise infrastructure, or application provider itself. That investigation often takes time because teams have to reproduce intermittent problems, collect evidence from separate tools, and hand cases between endpoint, network, and application owners.

Building Mobile Apps That Scale: A Business Leader's Perspective

Most mobile apps are built for the business as it exists on launch day. The trouble starts when the business keeps growing. A customer app that worked well for 5,000 users begins to slow down at 50,000. An ordering app that served one region struggles when the company expands nationwide. New features take months instead of weeks, and every release feels risky. These are not signs of bad luck. They are signs of an application that was never designed to grow.

Building a Network Appliance on RK3588? How Kiwi Pi 5 Pro and Orange Pi 5 Plus Compare

For gateways, edge nodes and remote monitoring boxes, the number of network paths a board offers often matters more than its benchmark score. Two popular RK3588 boards take noticeably different positions on that question.