Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Announcing LimaCharlie Email Security: Natively Integrated Into Your SecOps Stack

Co-founder & CCO LimaCharlie Email Security is generally available today. It protects Microsoft 365 and Google Workspace mailboxes from inside the same tenant, permission model, and data lake as the rest of LimaCharlie. A phishing email and the endpoint activity it causes can now be detected, investigated, and remediated in one place.
Introducing LimaCharlie Email Security: One Phish, Start to Finish

Introducing LimaCharlie Email Security. It connects to Microsoft 365 or Google Workspace through the provider's API, with no MX change and nothing in the delivery path, and shows the signals behind its verdicts. This walkthrough follows one malicious email from its 94/100 verdict through how the score compounds, a benign contrast with its measured processing timeline, the evidence, link analysis, response at the provider, hunting across the organization, groups and campaigns, user reports, the rule that caught it, policy, and email as telemetry for detection and response rules.

Building a bot takes five minutes. What it stands on took eight years. Introducing LimaCharlie Bots.

Co-founder and CCO We shipped bots in the LimaCharlie AI Terminal. You can create one in a few minutes: give it a role, pick a profile if you want one, and open a chat. I said this during our September Build Log demo and I'll repeat it here, because everything else in this post follows from it. The bot is the easy part.

How Soteria scaled its MDR practice on LimaCharlie

Soteria started as a consulting and advisory firm focused on penetration testing and incident response. Co-founder and managing principal Paul Ihme describes the company's growth from there as organic, expanding into virtual CISO work, offensive security, managed detection and response, and Microsoft 365 security products.

Why LimaCharlie's AI Sessions works with any model

Co-founder and COO I have been using AI coding tools since the beginning. Back around 2022, I built a RAG system that would return links to relevant documentation when users made a search request. Initially, I wanted the AI to answer the user's question directly, but at the time it would hallucinate so much that I didn't trust the output enough to put it in front of users. Instead, I had the AI return static links to the relevant documentation.

Run LimaCharlie AI Sessions on the model you choose

Co-founder and COO AI Sessions in the LimaCharlie web application now run on OpenAI, Google Gemini, and OpenRouter models in addition to Claude. Connect your own credentials, pick a provider per session profile, and the session behaves the same way regardless of which model is doing the work. Sessions run on Claude by default. Beyond that, you can connect any of the following with your own credentials.

AI in the MSSP SOC: From Pilots to Production

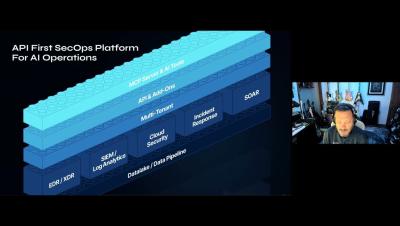
Every MSSP is under pressure to adopt AI, and most of the advice available is either vendor hype or generic guidance written for enterprise teams with one environment to manage. MSSPs face a harder problem: any AI they adopt has to work across dozens or hundreds of client stacks, respect tenant boundaries, and produce results an analyst can defend to a customer. In this session, Sr. Solutions Engineer Ken Westin lays out a practical roadmap for bringing AI into service provider security operations.

Intel Chat: Claude models reached real systems, an AI safety resignation & ShieldCrash [347]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.