Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Phishing Attacks Are Using Real Hotel Reservation Info to Target Travelers

Scammers are using legitimate hotel booking details to craft targeted phishing attacks, WIRED reports. Victims are far more likely to fall for a phishing attack if a message contains real information that they wouldn’t expect a scammer to know. According to researchers at Norton, this phishing campaign is targeting customers of at least 350 hotels and vacation rentals across 50 countries.
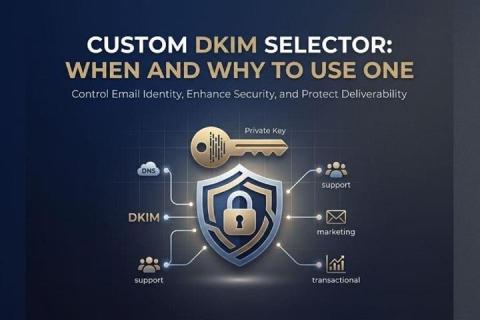
Custom DKIM Selector: When And Why To Use One

A DKIM selector is a label used by DomainKeys Identified Mail to locate the correct public key in DNS during the email authentication process. DKIM works by adding a DKIM signature to outgoing messages. That digital signature is created with a private key controlled by the sending service, while receiving systems use the matching public key published in your DNS records to validate the message.

8 Ways to Reduce False Positives in Email Security

False positives can disrupt inbound email security as much as missed threats by slowing business workflows and eroding trust in security controls. As phishing attacks become more convincing, many systems respond by tightening filtering thresholds. But without enough context, this can lead to overblocking, where everyday business communication is misclassified as suspicious. Reducing false positives requires more than adjusting filters.

Why Phishing Works

This article was originally published in Professional Security Magazine. Why are organizations still losing to phishing in 2026? Phishing has been the dominant attack vector for years. Despite this, organizations continue to be caught out by it. The UK government’s Cyber Security Breaches Survey 2026 confirms it remains the most prevalent and disruptive type of attack that businesses are facing. For those on the front line of incident response investigations globally, that finding is no surprise.

AI Alone Won't Stop the Breach: Why Email Security Needs Humans-on-the-Loop

2026 has officially become the year of speed, scale and support. The delta between a phishing email landing and a full organizational compromise has shrunk to mere seconds. The reality by the numbers: To close this window, your defense strategy must evolve into a two-step strategy of accuracy and automation.

Phishing Campaign Exploits Google AppSheets to Target Facebook Accounts

Researchers at Guardo Labs are tracking a major phishing campaign that abused Google AppSheet as a relay to send phishing emails. The researchers identified more than 30,000 Facebook accounts that were compromised by this campaign. Since the emails are sent from Google’s legitimate infrastructure, they’re much more likely to land in users' inboxes.