Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Patch Reliability Score: Make patch deployment decisions with confidence

Every Patch Tuesday starts the same way: New patches become available, and administrators begin answering the question, Is this patch safe to deploy? That answer rarely comes from a single place. Most administrators read the vendor's knowledge base article, look for known issues, monitor community discussions, and wait for early deployment feedback before rolling the patch out across the organization.
Featured Post

The first short-lifespan TLS renewal wave is closer than it looks

If your organization runs anything on the public internet, a mandate that changes how often you renew TLS certificates is already in effect. In March 2026, the maximum validity of public TLS certificates dropped from 398 days to 200. What fewer teams have worked out is that the first certificates issued under the 200-day cap start expiring at the end of September. That makes this autumn the first real test of whether your renewal workflows are ready for what the next three years will ask of them.

Tanium and Google Threat Intelligence bring Google-grade threat intel to the live endpoint

Security teams are under pressure to move faster, investigate more confidently, and make better decisions with fewer resources. But even the best security operations teams run into the same problem. They often do not have a reliable place to start. Threat hunting depends on high-quality intelligence and experienced analysts who know how to turn that intelligence into useful pivots. Alert triage depends on knowing which signals matter and which ones are noise.

Introducing Agentic SecOps: Live Endpoint Truth for the AI-Driven SOC

Security operations teams are being asked to move faster than ever. Adversaries are using automation, infrastructure changes by the minute, and the number of alerts, exposures, and investigative paths keeps growing. But too many SOC workflows still depend on scarce expert time. A senior analyst writes the query, translates the hypothesis, pivots across tools, validates the result, and then hands the finding off for action. The craft works.

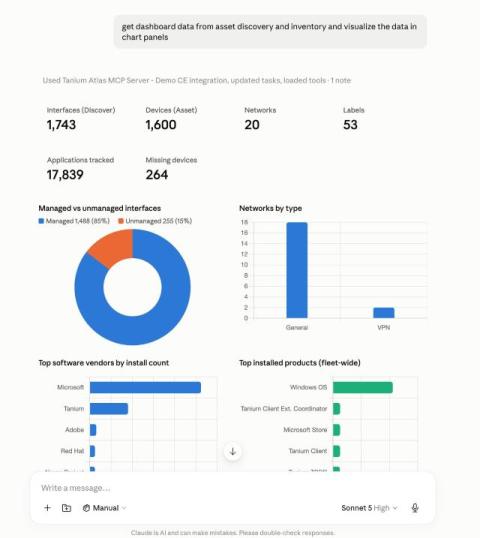
Bringing Tanium's real-time endpoint intelligence into enterprise AI workflows with MCP

Enterprise AI is quickly moving from experimentation to day-to-day operational use. Security analysts, IT operators, and platform teams are increasingly working inside AI-native environments — from Claude and Microsoft Copilot experiences to internally built agents and automation workflows. But there is a practical challenge: AI workflows are only as useful as the enterprise systems they can safely reach.

Dojo AI: Agentic security and cloud operations powered by AI-ready telemetry

You’re collecting more telemetry than ever, but chances are it hasn’t made your job easier. Fragmented data, disconnected tools, and manual investigations mean more noise, slower response times, and higher operational costs. The promise of AI is that it will solve it, but in most cases, you just end up trading noise for expensive hallucinations. Point an LLM at raw, unorganized log storage, and you get an assistant that burns through credits to produce generic, unreliable answers.


Unpacking the CrowdStrike 2026 Threat Hunting Report with CrowdStrike's Katie Blankenship

The CrowdStrike 2026 Threat Hunting Report is now live! The report sheds light on how our threat hunters and analysts hunt and defend against the world’s most sophisticated adversaries. It’s packed with stories from the front lines and trends that define the modern threat landscape.

7 Ways to Improve Microsoft Sentinel Detection Outcomes

See how Securonix Threat Analytics helps security teams improve detection coverage, reduce SOC engineering work, and maximize Microsoft Sentinel ROI. Microsoft Sentinel provides a strong foundation for security operations. As environments grow more complex, detecting sophisticated attacks often requires extensive engineering, custom KQL development, and ongoing content maintenance.