Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

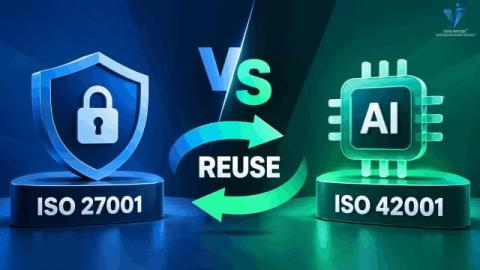
ISO 42001 vs ISO 27001: What Can You Reuse for AI Management?

If your organization already operates a mature ISO/IEC 27001 Information Security Management System (ISMS), you are not starting ISO/IEC 42001 from zero. Governance routines, document control, competence management, internal audit, management review, corrective action and parts of your risk and supplier processes may provide a useful foundation. But ISO/IEC 42001 is not an AI extension to ISO/IEC 27001.

Your Clients Already Deployed AI. Nobody Sold Them the Security for It.

Every vendor this year says the same thing: AI is transforming cybersecurity. True, and not useful. Here is the useful version. AI is doing two things at once. It is compressing the time between a vulnerability being found and being exploited, which is the part everyone talks about. And it is quietly installing a brand new attack surface inside your clients' businesses, which is the part nobody is selling against yet.

Secure agent access in development workflows with 1Password + NVIDIA OpenShell

1Password for NVIDIA OpenShell is available now as a developer preview in the 1Password nightly build. Connect a 1Password Environment to the OpenShell runtime and let your agents work with the systems it needs without exposing real credentials to the model.

Does a TLS Certificate Need a Common Name?

Technically: no. In practice: maybe. Lot’s of teams are experimenting with shorter duration certificates from Let’s Encrypt to get ready for the 47-day mandate. Those certs come with a big gotcha: no more Common Name. A modern browser is perfectly happy with a TLS certificate that has no Common Name. Your VPN or mail server might have other opinions. And since those are probably things you’d like to keep working, there’s a little more nuance to the answer.

Hunting Citrix NetScaler Zero-Days with Corelight

Citrix’s security bulletin CTX697096, the NetScaler security blog, and WatchTowr’s vulnerability FAQ describe an urgent situation for organizations using NetScaler ADC and NetScaler Gateway. Two vulnerabilities (CVE-2026-88771 and CVE-2026-88772) are known to be exploited. CISA confirms active exploitation globally and has added both to its Known Exploited Vulnerabilities catalog.

Cyber Loss When the Company Is Someone Else's Fourth Party

Third-party risk content is written from the customer's side. Assess your provider, tier your vendors, understand your concentration. ‍ A technology provider is on the other end of every one of those assessments, and its own incident propagates outward through contract rather than inward through remediation. The instinct is that the contracts therefore determine the loss. They determine the smaller half of it. ‍

The AI Act Duty That Applies Regardless of Risk Tier

Almost every obligation in the AI Act is keyed to a risk classification. Work out which tier a system falls into and the duties follow. ‍ Article 4 is not. It applies to providers and deployers of any AI system whatever it does, its subject is people rather than systems, and national authorities began supervising and enforcing it from 2 August 2026 while the high-risk regime moved to December 2027. It is the live one, and it sits outside the structure most governance programs are built on. ‍

AI Review of Privileged Material and the Waiver Question

Sending privileged material through an external AI service is a disclosure to a third party, and voluntary disclosure to a third party waives privilege. The reasoning is straightforward and a federal court has now applied it. ‍ A second federal court reached the opposite conclusion on the same question within days, on a distinction the first did not draw. The position is genuinely unsettled, and the parts that are settled point at configuration choices rather than at a prohibition. ‍

The Cybersecurity Directive That Reached Ten Times More Entities

The headline change in Europe's network security directive is scope. Directive (EU) 2022/2555 reaches an estimated hundred and sixty thousand entities across eighteen sectors, roughly ten times what its predecessor covered. ‍ The more consequential change is who decides. Under the previous regime a member state identified operators of essential services individually, through an assessment of criticality and dependency.

1Password for NVIDIA OpenShell: Give Agents Access Without Giving Them the Keys

Connect a 1Password Environment to the OpenShell runtime and let your agents work with the systems it needs without exposing real credentials to the model. Developers define their environment in 1Password and use the UI to provision an OpenShell credential provider. Secrets are mapped to OpenShell profiles, restricted to specific targets, and given an expiration date.