Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Ep 11 - Salt Typhoon Exposed: Breaking Down CISA Advisory AA25-239

In this special episode of The Cyber Resilience Brief, Tova Dvorin and Adrian Culley break down CISA Advisory AA25-239—a joint alert from CISA, NSA, FBI, and global cyber partners on the long-running Chinese state-sponsored threat group Salt Typhoon. Salt Typhoon has been quietly infiltrating critical infrastructure for years by exploiting outdated routers, weak credentials, and “living off the land” techniques like PowerShell, WMI, scheduled tasks, and built-in administrative tools—making them nearly invisible.
The CISO's Take: Securing the Future of Financial Services & More

New year, new threats… Except some aren’t so new; they’ve been years in the making. As the future of financial services evolves from relying on traditional banking to other platforms, securing our future requires practitioners to be more strategic than the threat actors after our assets. Join Aleksandr Yampolskiy and Jeff Lunglhofer for their take on: SecurityScorecard monitors and scores over 12 million companies worldwide.

The Business Logic Paradox: Hackers Are Your Best Architects #businesslogic #cybersecurity #api

Here is the truth: To exploit Business Logic Abuse, hackers must understand your application flow holistically. Your individual developers focus on clean code within their one block. The attacker studies the entire blueprint and finds the gaps and missing connections between those blocks. They are committed-spending months on reconnaissance to know your product better than your own team. You must adopt the attacker's mindset in your design stages!

Building Security With Customers, Not For Them - Jay Wilson x Garrett Hamilton | Insurity Case Study

Partnership over Procurement Why true collaboration between vendors and security teams is still rare — not because the intent isn’t there, but because most engagements stop at feature checklists. The alternative is more interesting: build together, solve together, and create solutions that fit how teams actually work rather than how tools assume they work. This mindset drove our work with Insurity — a real example of what happens when a security team engages deeply instead of treating tooling as a finished product.

Rogue Devices on Your Network: How Hackers Stay Invisible

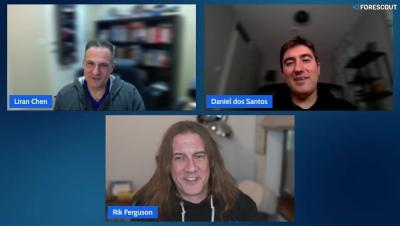
Cybercriminals and state-driven actors are getting smarter. Rogue devices, like stolen laptops or stealthy rogue routers, are bypassing traditional security measures and hiding in your network’s blind spots. In this discussion, experts Daniel dos Santos, VP of Forescout Research, Rik Ferguson, VP of Security Intelligence and Liran Chen, VP of Systems Engineering dive into.

Secure Your AI Workflows with Protecto's Data Masking API #startup #n8n

AI is evolving fast, but are your workflows truly secure? Most teams rely on DLP or redaction tools that strip sensitive data or block it entirely — but that limits your AI's potential. In this video, learn how Protecto’s SaaS Masking & Unmasking APIs help you process sensitive data (PII, PHI, PCI) securely, while staying compliant with GDPR, HIPAA, DPDP. No more trade-offs between data protection and powerful AI.

Intel Chat: Tomiris cyber-espionage, OpenPLC ScadaBR, NPM manipulates AI scanners & MuddyWater [273]

Support our show by sharing your favorite episodes with a friend, subscribe, give us a rating or leave a comment on your podcast platform. This podcast is brought to you by LimaCharlie, maker of the SecOps Cloud Platform, infrastructure for SecOps where everything is built API first. Scale with confidence as your business grows.

You Can't Have AI Security Without API Security: The Agentic Action Layer

AI agents run on APIs, and that is where most security programs have a gap. Salt Security Co-Founder and COO Michael Nicosia and CMO Michael Callahan explain why you cannot secure AI without securing the APIs underneath it. An AI agent uses an LLM to reason and an MCP server to broker calls out to other systems, and every one of those calls is an API interaction. Deploy one agent and the traffic multiplies. Deploy hundreds, and the internal east-west traffic climbs to several times what a pre-AI environment carried.

Securing AI Agents: How to See MCP Servers and A2A Traffic with Salt Security

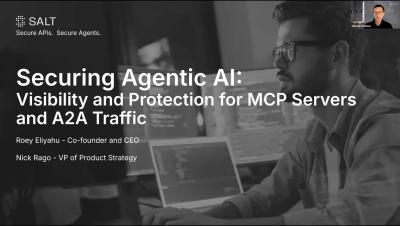
AI agents have moved past conversation into action. They book transactions, pull sensitive data, and chain tools together through the Model Context Protocol (MCP) and Agent-to-Agent (A2A) traffic. Every one of those actions runs on APIs, and that connective tissue is where the risk sits. Salt Security Co-Founder and CEO Roey Eliyahu and VP of Product Strategy Nick Rago walk through the risks in the agentic action layer and show what Salt does about them.

When Al Agents go Rogue: What you're Missing in your MCP Security

No Fluff, Just Real-World Threats This isn’t your typical marketing webinar. We cover what Agentic AI actually looks like in production, how MCP servers work to broker instructions, and what kind of new threats are emerging. Agentic AI isn’t coming. It’s already here. Autonomous agents are now operating in production environments, reasoning, remembering, and taking real actions across your systems. They’re not just generating content. They’re triggering workflows, modifying records, and making decisions. And they’re doing it over APIs.