Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

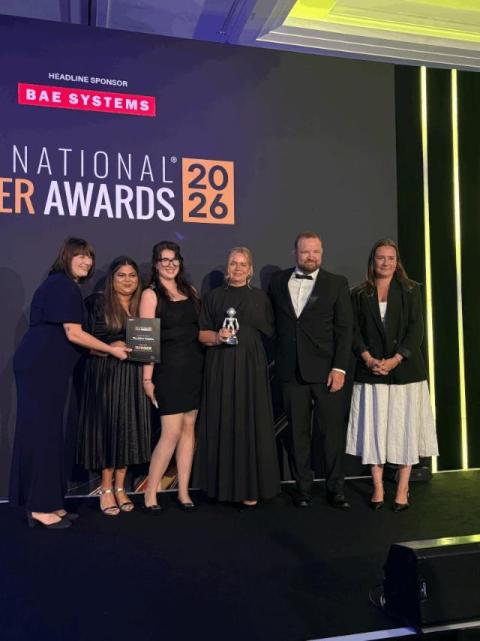
The Cyber Helpline Wins Not-for-Profit Award at 2026 National Cyber Awards

London, UK, September 29th, 2026 – We are thrilled to announce that The Cyber Helpline has been named Not-for-Profit Cyber Award winner at this year's National Cyber Awards. This marks our fifth win in the category, following wins in 2021, 2022, 2023 and 2024. Our team and volunteers were also recognised as finalists in three further categories: the Alan Turing Cyber Leadership Award, the Cyber Diversity Award and the Cyber Student of the Year Award.
Introducing Salt Claude Connect: Continuous MCP Server Visibility for Claude Enterprise

As AI adoption accelerates inside enterprises, security and IT teams are increasingly asking a foundational question: what exactly is connected to our AI, and what can it access? For organizations running Claude Enterprise, Salt now has a direct answer. Salt Claude Connect links Salt to Claude’s Compliance API and provides continuous, read-only visibility into the MCP (Model Context Protocol) servers connected to your Claude Enterprise organization.

Detectify Cyber Hygiene Index Report reveals that most critical vulnerabilities sit unfixed for months

The Detectify Cyber Hygiene Index Report H2 2026 measures something most reports ignore: not what happened after an attack, but what’s exposed right now, before one occurs. We analyzed anonymized data from a sample of +1290 organizations across the US, UK, and Nordics to understand how effectively they’re finding, monitoring, and closing vulnerabilities across their external attack surfaces.

FBI Winter SHIELD's Cybersecurity Controls Are Worth a Second Look

AI adoption is making everyone faster, including the attackers we as cybersecurity practitioners are competing with. While the attackers are getting faster thanks to AI, it’s not changing why most preventable breaches happen. That part is remaining consistent, for better or worse.

Mobile App Security: Reverse-Engineering APKs and IPAs to Uncover Hidden Attack Vectors

Buried in OpenAI’s evaluations of its GPT-6 Astra model sits a finding that mobile teams should sit with for a minute. The model reverse-engineered compiled software well enough to escape a browser sandbox and chain privilege-escalation flaws on a hardened operating system, according to the company’s published evaluations. Reading compiled binaries used to be specialist work priced in weeks, and now it’s something machines do quickly and well.

Beyond the Scanner: How Verified PoC exploits Prove True Business Risk

On September 1, OpenAI announced that its new model, GPT-6 Astra, had become the first to cross the “Critical” cybersecurity threshold in the company’s Preparedness Framework. Most coverage focused on the safety implications, and fairly so, but buried in the announcement sits a benchmark result that should change how every security leader reads their next vulnerability report.

Jev's Paradox: The hidden cost of cheap AI decisions

This article was first published on LinkedIn. Consider a cybersecurity alert for a potentially malicious PowerShell script that downloads and runs a file. An AI agent in a security operations center (SOC) can handle it by picking from a fixed set of actions: close the alert as benign, collect more evidence, or send it to an analyst. Before letting the agent act on such alerts, the SOC needs to know how often it picks correctly and whether its confidence helps identify its mistakes.

What Are Managed Services, and Why Can Network IT Teams Rely on Them?

That might sound like a trick question since it’s what we do as a managed infrastructure services provider. But it really isn’t. Here is the quick answer: Managed services let organizations outsource day-to-day IT operations, including networks, security, connectivity, and policy management, to a specialized provider.