

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

DragonForce Ransomware Profile: From Affiliate Program to Cybercrime Cartel

When people discuss DragonForce, two distinct names usually come up: DragonForce Ransomware and DragonForce Malaysia. To set the record straight, the ransomware operation isn't necessarily the same entity as DragonForce Malaysia. DragonForce Malaysia operates as a politically driven hacktivist collective known for pro-Palestinian campaigns, defacing websites, launching DDoS attacks, and leaking data.
Power Grid Attacks Aren't New. So Why Are They So Electric Right Now?

In late July 2026, 36 municipal waste and water systems across Minnesota were targeted in a cyber attack. The attackers targeted Programmable Logic Controllers (PLCs) that were in control of pressure, pumps, and chemical dosing. When the news broke, it felt like it was everywhere. This was an attack on critical systems, systems that we require and use daily. But cyberattacks on U.S. critical infrastructure systems like water, hospitals, sewage, gas, and electricity aren’t new.

The Attribution Trap: What Happens When Threat Actors Manipulate the Story of an Attack?

Imagine waking up Monday morning to discover you’ve been breached. The attacker has stolen sensitive financial data, set up persistent access, and then greets you with a lovely ransom note at 8:00 a.m. demanding money in exchange for the encryption key. Immediately, you reach out to your security operations team, and they quickly begin assessing the damage and reviewing the breadcrumbs left behind.

Know What's Actually Happening to Your Suppliers, Not Just When Their Names Show Up in Threat Data

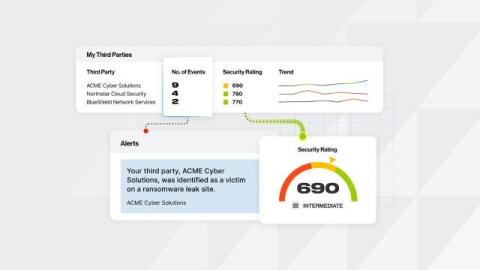
A vendor can pass every questionnaire you send it and still be the reason you end up in a breach report. That's the gap most third-party risk programs live in today. According to the 2026 Verizon Data Breach Investigations Report, 48% of breaches now involve a third party, up from 30% the year before and 15% the year before that. But most organizations still manage that risk with periodic assessments and separate threat feeds. Those methods can tell you whether a supplier passed a review last quarter.

CVE-2026-88771 and CVE-2026-88772: Two Critical Citrix NetScaler Flaws Under Active Exploitation

Citrix disclosed two critical vulnerabilities in NetScaler ADC and NetScaler Gateway that are already being exploited in the wild. CVE-2026-88771 allows unauthenticated attackers to run commands on an affected appliance, while CVE-2026-88772 can lead to remote code execution or denial of service when DTLS is turned on. Both received a CVSS v4.0 score of 9.5, and CISA added them to its Known Exploited Vulnerabilities catalog.

Identity Risk: 5 Access Pathways Emerging Across Threat Intelligence

It’s not a secret that phishing, stolen credentials, and human error remain some of the easiest ways for attackers to get into an environment. Identity has become one of the biggest attack surfaces for organizations today because sometimes, all an attacker needs to do is log in. That access can come from valid credentials, stolen sessions, exposed tokens, compromised service accounts, or abused application permissions.

While Defenders Watch the Zero-Day Clock, Attackers Are Looking Elsewhere

When Anthropic introduced Mythos Preview, the story practically wrote itself. Here was a frontier AI model taking work that once required researchers and threat actors a lot of time and compressing it into hours. Mythos demonstrated the ability to find and exploit vulnerabilities across major operating systems and browsers. In controlled testing, it produced a working Firefox code-execution exploit in less than an hour and developed eight in roughly 12 hours.

CVE-2026-76460: A critical Cisco ISE authentication bypass under active exploitation

Cisco has disclosed a critical authentication bypass affecting Cisco Identity Services Engine (ISE) and Cisco ISE Passive Identity Connector (ISE-PIC). Tracked as CVE-2026-76460, the vulnerability allows an unauthenticated, remote attacker to send a crafted request to an affected API endpoint and bypass the web-based management interface. The vulnerability received the highest possible CVSS v3.1 score of 10.0.

From CVE Disclosure to Internet-Wide Exposure: How Bitsight Uses AI to Accelerate Product Fingerprinting

When a new CVE drops, getting notified is the easy part. The real challenge comes right after. Depending on how your organization is set up, different teams have to scramble to figure out if you're actually using the affected product, which specific versions are exposed, whether it's lurking anywhere in your subsidiaries or vendor ecosystem, and how urgently you need to patch it.

13 essential cybersecurity frameworks, standards, and regulations explained

Security teams rarely work from a single rulebook. They may use the NIST Cybersecurity Framework to organize the program, ISO/IEC 27001 to build a formal management system, SOC 2 reports to assess vendors, and laws such as HIPAA, GDPR, DORA, or NIS2 to meet legal obligations. Those names are often grouped together, even though they serve different purposes. Some provide guidance. Some can be certified or independently assessed. Others are contractual requirements, laws, or mandatory sector standards.