

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to Audit AI Compliance from Both Sides of the Table

The tricky thing about AI compliance is that most organizations are going to experience it from both sides. You need to be able to explain how AI is being used inside your own organization, what it can access, and how you're managing the risk. At the same time, you need to understand how your vendors are using AI and whether that introduces new risk into your environment.
From Hotspots to Lookalike Domains: 3 Phishing Tactics to Watch

In our previous “ABC’s of ‘ishing” posts, we explored how attackers use social media, calendar invites, fake CAPTCHA challenges, and other trusted tools to deceive users. This next installment looks at three phishing techniques that continue to put organizations and individuals at risk: evil twin phishing, domain spoofing, and email phishing.

'The Gentlemen' Profile: Why This Ransomware Group Wants In Before It Locks You Out

The Gentlemen is a financially motivated ransomware group that combines data theft with encryption to increase pressure on victims. They first came onto the threat scene in July 2025. Rather than relying on encryption alone, the group exfiltrates sensitive business data before locking files, leaving organizations to deal with both operational disruption and the risk of stolen information being exposed.

New Bitsight Research Shows AI Abuse Is Moving Beyond the Jailbreak Prompt

Jailbreak prompts (i.e. prompts designed to remove or bypass the guardrails and rules that govern AI systems, like LLMs) prompts have been circulating for years. At first, a lot of it was pretty simple: copy a prompt, tell the model to ignore its rules, and see what happens. It was also largely noisy, unverified, and often didn’t work. But the noise was still telling us something. Threat actors were beginning to study AI systems the same way defenders were, and over time, the goal started to change.

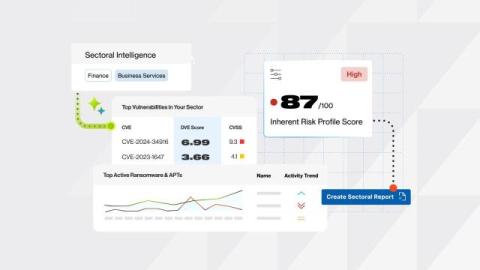
Focus on the Threats That Actually Matter to your Organization with Sectoral Intelligence

Not every threat matters equally to every organization. A newly discovered APT or ransomware group targeting European automotive manufacturers is definitely worth paying attention to, especially if you’re in that sector. But if you’re a financial services firm in California, it’s probably not an immediate priority. You might look into it, track its activity, and assess whether it could become relevant.

Insurance Is Still in the Crosshairs: What Recent Dark Web Chatter Says About Sector Targeting

Insurance has always been a data-rich industry. But recent threat intelligence makes it clear that attackers are not only going after insurers because they are large organizations. They’re going after them because insurance touches some of a threat actor’s favorite things: money, identity, healthcare, legal claims, third-party relationships, and highly sensitive customer records.

The Invisible Expansion of the Attack Surface: Shadow AI, MCP, and Third-Party Risk

AI adoption is moving faster than most of us anticipated and, more importantly, faster than most organizations can govern it. Organizations are implementing the use of AI-enabled applications, browser extensions, coding assistants, and automated agents to enable employees to work faster. In many cases, these tools are adopted without security review, procurement approval, or a clear understanding of where organizational data is being sent.

Thousands of Exposed Fuel Gauges Just Left the Internet

Most of the exposure research we publish goes one way. We count some category of internet-exposed devices, the number is bigger than you hoped, and it is climbing. Webcams. Industrial control systems. NTP servers old enough to vote. The story is almost always "there is more of this exposed than there should be, and it is getting worse.".

How Bitsight Helps Financial Institutions Align With Bank Negara Malaysia's RMiT Policy Document

Financial institutions are not short on cybersecurity policies, frameworks, or regulatory requirements. Turning those requirements into a living risk management program can be challenging. Organizations need a program that can keep pace as technology environments expand, cloud adoption grows, third parties are added, and external exposures change. Especially as the threat landscape continues to evolve.