Effectively utilizing a risk register allows your organization to anticipate and overcome challenges with confidence. No GRC program is failproof, which is why it’s so critical to take a thorough look at potential risks and remediations. To make sure you’re starting on the right foot, we’ve provided a free, downloadable risk register template you can use once you have a better understanding of what it does.
Welcome to our guide on ISO 27001 compliance! We’ll cover everything you need to know about ISO 27001, including its clauses, the preparation & audit processes, costs, and best practices. Let’s get started!
New research from SecurityScorecard found that 98% of organizations have at least one vendor that’s had a breach in the last two years. Although this doesn’t necessarily mean affiliated organizations were affected by the breaches, it does emphasize the extensive range of potential exposure to indirect risks. Now more than ever, it’s crucial for vendors to develop a deep understanding of security questionnaires and to implement best practices.
Our team has been hard at work creating updates and new features just for you, see what we’ve been up to over the last month.
For SaaS applications and cloud service providers (CSPs), maintaining compliance with FedRAMP requirements is critical to the bottom line. It means the difference between working with U.S. government agencies—or not. But as one might expect from a bureaucratic process, getting FedRAMP authorization is complicated and takes time. Before starting the FedRAMP approval process, teams and company leaders must understand the required steps, prepare thoroughly, and muster their patience.
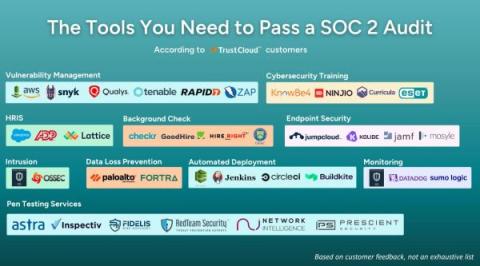
Achieving SOC 2 compliance often necessitates the use of specialized tools and software to address specific application and data security measures, but which ones are the best to get the job done? We asked our customers which tools they used and compiled their answers below. Now, let’s break down the tools that have helped our customers achieve compliance excellence, so you can, too. Tools or services marked with * denotes a partner or integration.
After tons of hard work, your company has successfully completed a SOC 2 audit and received a well-deserved SOC 2 report! Congratulations! Receiving your SOC 2 attestation is no easy feat, and it’s a significant milestone that demonstrates your company’s commitment to security and trust assurance. If you’re not sure what to do next, no worries – the hard part is done.