Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Conquering the Chaos of Vulnerability and Exposure Management at RSAC Conference 2025

Recently, industry analyst Jon Oltsik outlined a critical shift underway in cybersecurity: the move toward a threat-informed defense. As Oltsik describes, organizations are beginning to strengthen the intersection of vulnerability scanning and threat intelligence, using AI to bolster asset classification and risk scoring. This evolution is essential as enterprises seek to move beyond fragmented security practices and build a more cohesive exposure management strategy.
Supporting CTEM Scoping with Exposure Assessment Platforms

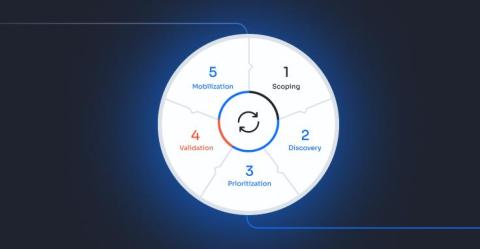
In our recent article on Continuous Threat Exposure Management (CTEM), we highlighted how exposure assessment platforms (EAPs) like Nucleus can support several critical phases of the CTEM framework. In that article, we intentionally separated the scoping step from the other technology-dependent CTEM stages. Scoping begins as a business- and process-driven exercise. However, doing scoping well and at scale relies more on having the right technology.

Achieving Continuous Exposure Management in Cloud-Native Environments

In this webinar, "Achieving Continuous Exposure Management in Cloud-Native Environments," Tally Netzer and Aaron Unterberger from Nucleus dive deep into how modern cloud architectures impact vulnerability and exposure management. You'll learn: Why traditional vulnerability management falls short in cloud-native, ephemeral environments. How fragmented visibility and unclear ownership disrupt effective security practices.

GPSec Boston 2025 - CTEM: How to Start When You Haven't Started

What does it really take to start a Continuous Threat Exposure Management (CTEM) program—especially if your organization hasn’t formally begun? In this GPSec Boston 2025 session, Scott Kuffer, COO and Co-founder of Nucleus Security, joins Chris Peltz, Director of Security Strategy at GuidePoint Security, to demystify CTEM by stripping away the buzzwords and breaking down the practical steps for getting started.

POAM Process Automation: Breaking the Manual Grind

Plans of Action and Milestones (POAM) play a critical role in public sector cybersecurity. In this webinar with government IT solutions provider Carahsoft, we break down the challenges security teams face when implementing POAMs, sharing real-life examples of where things go wrong and why. As part of the presentation, we also cover the intensive math of POAM programs: people, systems, and time.

Continuous Threat Exposure Management and the Role of Exposure Assessment Platforms

Traditional vulnerability management is broken. It is ineffective. The process of scanning for software vulnerabilities, prioritizing based on CVSS scores, and fixing what you can has become an endless patch cycle. The need for a better approach is clear. Different scanning tools are creating millions of alerts, obscuring critical risks within the noise. Organizations need to go beyond finding and patching vulnerabilities and opt in to a more effective approach to managing exposures.

Managing Cloud Exposures Just Got Easier: Introducing Nucleus Cloud-Native Vulnerability and Exposure Management

Every day, security teams are expected to manage risks in cloud environments that they don’t fully control, can’t always see, and that are constantly changing. Cloud-native assets—such as container workloads, autoscaling groups, and serverless functions—are highly dynamic, appearing, disappearing, and evolving in response to demand and functionality changes.

Is Enterprise Risk Posture Better or Worse Today?

Measuring enterprise risk posture—its overall security readiness and resilience—is a complex challenge. Advanced security solutions, such as automated vulnerability management tools and unified risk dashboards, enable organizations to defend their networks with unprecedented efficiency. The rapid expansion of cloud environments and the intricacies of modern IT infrastructures, however, present an increasingly dynamic attack surface.