Introducing XDP-optimized denial-of-service mitigation
In this article, we’ll explore Calico’s denial-of-service (DoS) mitigation features, including XDP-optimisation support introduced in Calico v3.7.


In this article, we’ll explore Calico’s denial-of-service (DoS) mitigation features, including XDP-optimisation support introduced in Calico v3.7.
In an ideal scenario, security would be baked into the development process from the very beginning. Security teams would primarily exist to verify that best practices have been followed at every step in the process. In practice, security is an enormous challenge for most organizations. This challenge is compounded by the increasingly complex and fast-paced nature of modern service-oriented architectures, such as Kubernetes.
Congratulations Twistlock! One of the best signs of an emerging market is when existing, massive players are willing to put hundreds of millions of dollars on the line to get into that market right now. Given today’s Twistlock acquisition by Palo Alto Networks, and other recent acquisitions like Heptio/VMware, we believe this is happening in the cloud-native market. Congratulations to Twistlock on their success.
Container orchestration and cloud-native computing has gained lots of traction the recent years. The adoption has increased to such level that even enterprises in finance, banking and the public sector are interested. Compared to other businesses they differ by having extensive requirements on information security and IT security. One important aspect is how containers could be used in production environments while maintaining system separation between applications.
We are excited to announce the new security capabilities of Tigera Secure Enterprise Edition 2.4. This release enables enterprise security teams to extend their existing zone-based architectures and easily connect to external resources. The highlights include DNS Policies, Threat Defense, Compliance Dashboard and Reporting, and easier installation options.
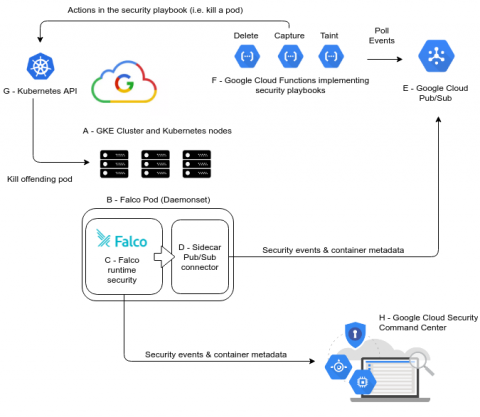
In this blogpost we will demonstrate how to build a complete GKE security stack for anomaly detection and to prevent container runtime security threats. We will integrate Falco runtime security engine with Google Cloud Functions and Pub/Sub.
Recently, a member of the Falco community privately disclosed a capacity related vulnerability which, under circumstances where a malicious actor has already gained access to your system, could allow the actor to further bypass Falco’s detection of abnormal activity. The final details are still being worked out, but we believe the CVE will be classified as Medium severity according to the CVSS methodology.
We are happy to announce the release of Falco 0.15.0. This release incorporates a number of improvements, as well as bug fixes, and rules updates. This release also includes a mitigation for CVE-2019-8339, and all users are encouraged to update to this release. You can find more details about the features and improvements in the release notes, but below are a few highlights.