Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Taming wild code with Tines 3B: The Headspace story

AI changed who can build, and now IT teams must navigate a new challenge. Employees across the business are creating apps, agents, and automations faster than ever. The result is a wave of "wild code": unmonitored workflows that solve immediate problems but bypass traditional governance and operational ownership. Without the right platform to centralize visibility and ensure safety, you face blind spots that compromise your most important workflows.

What's new in Tines: July 2026 edition

July was an exciting month in the world of Tines. We launched Tines 3B, the single, secure environment for every team’s apps, agents, and automation. It’s a new platform where everyone can build, while you safely run and monitor your organization’s most important work. The Tines platform you already know is now called Tines Stories, and we’ll continue to invest in, support, and develop it.

What's New in Risk Automations: 4 Templates for Vendor and User Risk

Most vendor onboarding and app access work is waiting and follow-ups. Waiting for someone to notice a form came in, assign a tier, chase a questionnaire, or dig up the context behind a Slack request. Risk Automations workflows remove that wait and automate the follow-up. A trigger fires, and the workflow runs to a concrete outcome: a ticket created, a message sent, a risk tier assigned. To make those workflows easier to launch, Risk Automations includes an ever-expanding template library.

From executive order to operational reality: a federal AI SOC blueprint

The June 2, 2026 White House Executive Order on Promoting Advanced Artificial Intelligence Innovation and Security has officially set the clock ticking. With mandates requiring CISA and federal agencies to deploy AI-enabled defensive tools on civilian systems, the directive for Federal CIOs, CISOs, and SOC Directors is clear: AI adoption is an operational requirement to effectively defend federal networks.

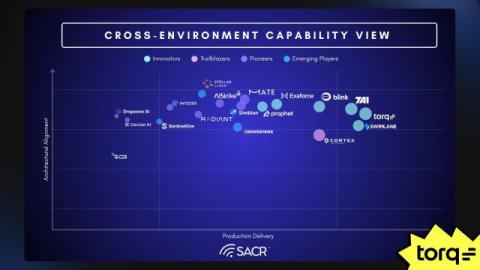
Torq Named a Leading Innovator in SACR 2026 AI SOC Market Report

Software Analyst Cyber Research (SACR) just published its 2026 AI SOC Market Report, offering an independent assessment of vendors competing in what has rapidly become the most consequential category in enterprise security. Torq features prominently, and the report’s framing is worth unpacking because it illuminates what makes the AI SOC category hard to evaluate and why Torq’s approach is consequential.

Torq SOC Brain: The AI SOC That Learns, Not Just Remembers

Back in June, I wrote a blog making the case that agentic triage alone isn’t an AI SOC. The way I see it, that’s like saying triage is the only responsibility of a SOC team. But as we know, the SOC’s responsibilities extend far beyond that, and these triage-only solutions don’t investigate threats, contain them, or close cases. That work is still left to the SOC team; the bottleneck is just shifting.

Introducing Tines 3B

Your teams are moving fast with AI — but is IT and Security able to see what's actually being built? IT and AI leaders are facing a career-defining challenge right now: AI-generated code and shadow AI spreading faster than anyone can track. Introducing Tines 3B — a single, secure environment that gives employees the freedom to build with AI, and gives IT and security the control to govern that work safely.