Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

7 Things People Get Wrong About Quantifying Cyber Risk

Most explanations of financial cyber risk modeling cover what it is. The more useful material is what surprises people once they have a model in front of them, because several of the outputs run against intuition and get misread in predictable ways. ‍ Seven of those are worth knowing before the first results arrive. None requires a statistics background, and each one changes how a number should be read or reported. ‍
AI Governance Tools and the Audit Trail Problem

An AI governance platform demo shows you the present. Compliance posture at seventy-nine percent, four controls needing attention, a register of systems with owners attached. Every figure describes today, and the demo is persuasive precisely because today is legible. ‍ An audit asks a different question.

How to prevent ransomware damage: a 12-step checklist for IT teams and MSPs

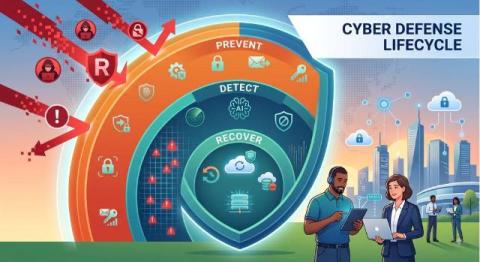
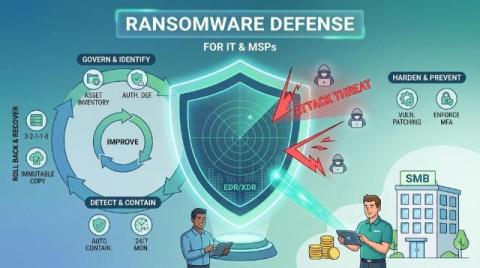
No combination of controls guarantees that ransomware actors will never gain access or cause any impact. What the 12 controls below do is reduce the attacker's opportunities, accelerate containment and preserve the ability to restore operations without relying on ransom payment. Think of ransomware resilience as a continuous lifecycle rather than a fixed sequence: govern and identify, harden and prevent, detect and contain, roll back and recover, and improve and patch.

SharePoint CVE-2026-55040 Actively Exploited: AI-Discovered RCE Chain

CVE-2026-55040, a critical SharePoint authentication bypass, is now being actively exploited. A proof-of-concept went public on August 11. Within 24 hours, threat intelligence firm Defused confirmed exploitation attempts against its SharePoint honeypots using that same PoC. Over 8,500 SharePoint servers remain reachable from the open internet, putting unpatched instances at immediate risk.

Application Layer Firewall: How It Works and Why It Matters

Your SOC dashboard shows a successful login from a normal user account. The connection uses HTTPS, the destination is an approved web server, and the network firewall allows it. Inside the request, however, an attacker has placed a SQL injection payload in a login parameter. Nothing is wrong with the perimeter firewall. It has been asked to answer a question it wasn't designed to answer.

What an Open Control Weakness Costs You Every Month

Security programs price control work as an investment decision. What does the fix cost, what does it remove, does the return justify the spend. The framing answers whether to do something and says nothing about the cost of the interval before it gets done. ‍ An unimplemented control accrues expected loss for every month it stays unimplemented.

OpenTelemetry and AI Governance: Where the Standard Stops

OpenTelemetry graduated from the Cloud Native Computing Foundation in May 2026, which formally settled a question the industry had answered informally years earlier. It is the standard way applications emit telemetry, second only to Kubernetes in contributor volume, and native across every major observability backend. ‍ A security and governance company has a specific reason to care.

Ransomware protection for businesses and MSPs: the complete guide

Ransomware protection is a coordinated set of controls that reduces the likelihood of compromise, detects and contains malicious activity, protects recovery infrastructure and restores operations when an attack succeeds. It spans identity security, vulnerability and patch management, endpoint protection, EDR or XDR, incident response, targeted rollback, immutable backup and disaster recovery. No single control covers the complete ransomware lifecycle.

Cyber Security for Lawyers: A Practical Compliance Guide

You're in the middle of a normal week, and a partner calls because a client can't open a shared matter folder. Then the help desk finds encrypted files, a strange login from overnight, and an inbox rule that forwarded privileged emails outside the firm. That's the starting point for cyber security for lawyers, not a policy memo, and it's why your firm needs controls that protect confidentiality, preserve evidence, and prove due care when the pressure is on.

What is Managed Detection and Response (MDR)?

As technology grows at a rapid pace, many organizations have switched to new ways of working. Now, hybrid work environments are extremely common, with many organizations hiring employees who work remotely. And then there is the rapid growth of artificial intelligence (AI), which has further changed the way operations are carried out in organizations. Technology has significantly improved the efficiency and accuracy of work, but it has also increased the attack surface.