Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Easiest Way to Get Hacked: Open Introspection. #graphql #businesslogic #apisecurity #rbi

The RBI incident (Burger King, Tim Hortons) proves that BLA often results from a cascade of simple flaws, not one complex attack. The key mistake: GraphQL Introspection was enabled. This gave the attacker the full API blueprint - the map needed to find the open registration validation flaw and execute a massive data leak. Action Item: If you have GraphQL, check your production settings now. Disable Introspection. Don't hand the attacker the map to your castle!
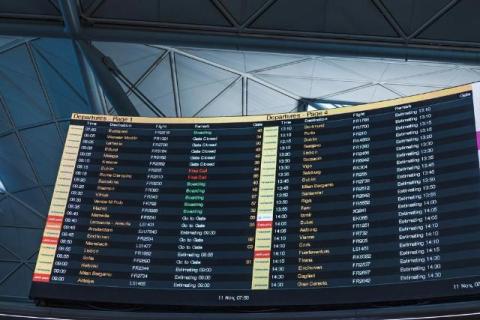
Digital Signage Security: The IoT Vulnerability Hiding in Plain Sight

Walk through any airport terminal, hospital corridor, or corporate lobby, and you will encounter digital signage displays. They announce flight departures, guide patients to their appointments, and broadcast company news to employees. These screens have become so common that we barely notice them anymore. And that invisibility is precisely the problem. While cybersecurity teams focus their attention on firewalls, endpoint protection, and cloud security, digital signage systems often slip under the radar as low-priority assets. Hackers, however, have taken notice.

How Do Credit Cards Get Hacked? Here Are 5 Surprising Answers

Picture this: you didn't click on any sketchy links, download weird apps, share your OTP, or even use your card recently. Then out of nowhere, your phone lights up with alerts that US-based companies like Best Buy, Bark Co, and Insomnia Cookies all made charges using your card. So, you call your bank in a panic and freeze your card. The whole thing may feel confusing, stressful, and honestly, kind of scary.

Cyber Startup Frenetik Launches with Patented Deception Technology That Bets Against the AI Arms Race

While most cybersecurity companies pour resources into AI models, massive compute, hoovering up all the data, and enhanced analytics to detect and prevent threats, Frenetik, a Maryland cyber startup, is betting on something simpler: making sure attackers don't know what defenders know. The company emerged today with a fundamentally different approach using novel cyber deception and a newly issued U.S. patent to back it.