Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

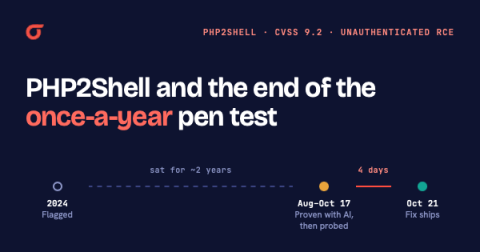
PHP2Shell and the end of the once-a-year pen test

On October 21, 2026, PHP shipped emergency fixes for two flaws that let anyone on the internet run code on a PHP web server, with no login. The weakness behind them had been flagged in 2024 and then sat, partly because nobody had proved it was exploitable. In 2026, researchers working with AI models proved it within days. Exploit attempts started before the fix shipped, and details leaked a day ahead of schedule. That sequence is the real story of PHP2Shell. The bug matters, but speed matters more.
Appknox MCP: Find, Fix and Verify Mobile App Vulnerabilities Without Leaving Your IDE

Appknox MCP agent connects your AI coding agent to your Appknox scan results and KnoxIQ analysis. Your agent triages findings by exploitability, fixes the code in your repo and verifies each fix with a re-scan, inside Claude Code, Cursor, GitHub Copilot, Codex or Windsurf. Your AI coding agent already writes features, refactors code and fixes bugs. It can't see your security findings. So when a scan flags a vulnerability in your mobile app, the fix still starts by hand.

Mobile-First Companies Have the Most to Lose Under the Cyber Resilience Act, and the Most to Gain

Since 11 September 2026, an actively exploited flaw in your app starts a 24-hour reporting clock under the EU's Cyber Resilience Act. That's expensive if you don't know what's running, and an edge if you do. For most companies, an app is a channel. For a mobile-first company, it is the business: the bank branch, the checkout counter, the boarding gate, the clinic waiting room. Until this year, however, the law mostly treated it like a channel.

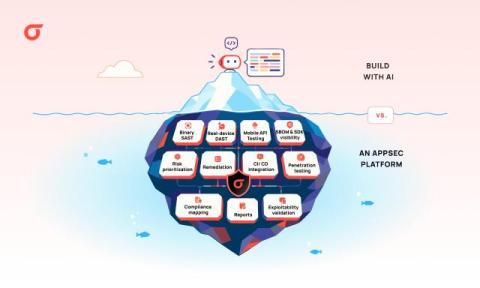
Why Buy a Mobile AppSec Platform Instead of Building With AI?

AI has lowered the cost of building mobile security tooling to near zero. However, it has not lowered the cost of operating it. Building a scanner is now a weekend project, while sustaining detection accuracy, threat research, real-device infrastructure, and developer trust across years remains a full organizational commitment. That distinction is the entire build-versus-buy question in 2026, and most evaluations get it wrong by measuring the wrong thing.

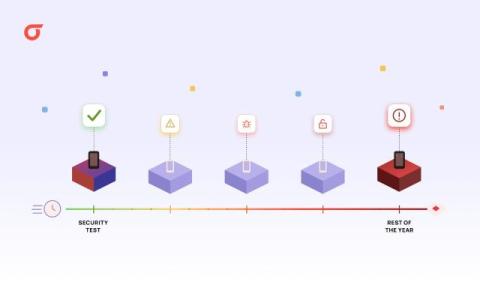
Why Annual Mobile App Security Testing Is Not Enough on Its Own

Annual testing secures a moment. Your app keeps changing. Here is how to cover the interval between assessments. An annual penetration test answers a precise question. Was this version of this application secure when a skilled tester examined it? That answer has real value. It is independent, deep, and finds business logic flaws that no scanner will ever surface. It is also a photograph.

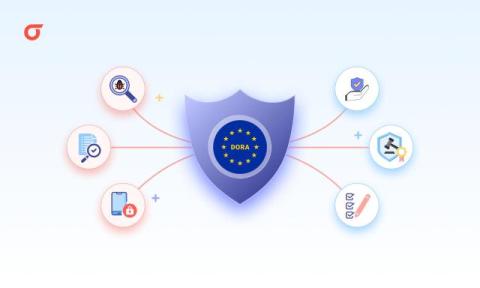
DORA Compliance for Mobile Apps: Mapping Security Findings to Regulatory Requirements

DORA compliance for mobile applications is the process of identifying, testing, and documenting mobile ICT risks in line with Regulation (EU) 2022/2554, covering Articles 8, 9, 10, 24, and 25, through vulnerability assessments, security testing, and audit-ready evidence generation that financial institutions can present to regulators, auditors, and internal governance bodies.

Best MAST Tools in 2026: Top Mobile Application Security Testing Platforms Compared

Your mobile app ships as a compiled binary to millions of devices you do not control. Anyone can decompile it, extract hardcoded secrets, reverse-engineer the logic, and exploit business-logic flaws that no automated scanner catches. Yet most security programs still treat mobile as an afterthought, running a web-focused SAST tool against mobile source code and calling it done. That approach misses platform-specific risks.

Appknox vs Runtime-Only Mobile Testing Tools: What Dynamic Analysis Cannot See Before the App Runs

Frida hooks into your app's running process in seconds. It intercepts API calls, dumps the keychain, bypasses SSL pinning, and reveals exactly what the app does at runtime. Frida is also the tool attackers use to do the same things to your users. Runtime testing tells you what happens when an app runs under test conditions. It does not tell you whether the app can resist those same tools when an attacker uses them in production. That answer is not in the runtime session. It is in the binary.

Appknox vs ASPM Vendors: What Application Security Posture Management Misses in Mobile App Security

Your ASPM dashboard shows your mobile security posture. The score reflects what your integrated testing tools found. It does not reflect what they could not test. For mobile apps, the gap between those two things includes the compiled binary, the third-party SDKs linked inside it, and what the app does at runtime on a real physical device. None of that data enters an ASPM dashboard built on source code scan results. The posture view looks complete. The coverage is not.

Best Mobile API Security Testing Tools for CI/CD Pipelines

Your pipeline has an API testing stage. Your scanner runs on every build. A finding list comes back clean. And then something gets exploited in production that your pipeline ran past 47 times without flagging. Here's what happened: endpoint validation passed. Security didn't. They are not the same thing. Here's what that box doesn't capture: APIs don't fail in clean test environments.