Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

New Research: Spike In DNS Queries Driving Phishing and Cyber Attacks

New analysis of DNS queries shows material growth in phishing, malware and botnets and offers insight into how many threats the average person experiences. Most of the reports I cover use detection on an endpoint, a security solution, or the corporate network for their analysis, but the 2024 Annual Security Report from DNSFilter feels a bit more impartial because it uses DNS queries to determine whether whether malicious activity is occuring.
Troubleshooting DNS issues in Kubernetes: Investigate and reduce NXDOMAIN (domain does not exist) responses

NXDOMAIN, indicating the non-existence of a queried domain, poses significant challenges within Kubernetes, impacting application functionality, service communication, and overall cluster stability. Investigating NXDOMAIN responses in Kubernetes is vital for sustaining the reliability, performance, and security in a containerized environment.

Cracking the Code: How to Identify Devices via MAC Addresses Online

Did you know that each device on a network has a unique MAC address? This ID allows us to identify devices quickly in the digital world. MAC addresses help us keep networks safe, manage devices efficiently and address issues as quickly as possible.

Understanding DNS-Based Threats and How They Impact Your Business

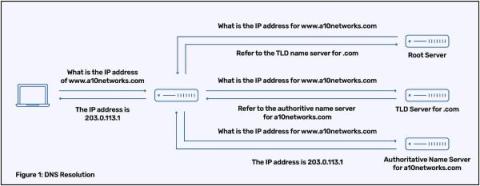
Cybersecurity, DNS (Domain Name System), and your company are interconnected topics in the field of network security. Protecting a company’s cybersecurity, including its DNS infrastructure, is of utmost importance in today’s digital landscape. DNS is responsible for translating user-friendly domain names into machine-readable IP addresses, allowing devices to communicate with each other over the internet.

How Egnyte Migrated Its DNS At Scale With No Service Disruptions

Egnyte, as a custodian of vast volumes of customer data and files, manages billions of files and petabytes of data originating from millions of users. With a system processing over a million API requests per minute, spanning metadata operations and analytical queries, the need to balance throughput and maintain exceptional service quality is paramount.

How to Find Out Hosting of Website?

The hosting provider is an important piece of a website's backend infrastructure. But if you come across a website, how can you find out which company or service hosts it? This article will outline several methods to identify the hosting provider behind any website, including the use of online tools, DNS record analysis, source code inspection, and contacting the website owner.

Enhance Threat Detection and Response with Intel DNS

ThreatQuotient and Infoblox recently hosted a webinar, where they demonstrated how the combination of DNS Intel and the use of a Threat Intelligence Platform (TIP) help to improve threat detection and response capabilities. Infoblox specializes in DNS Intelligence where their internal experts analyze, process and qualify DNS intelligence (analyzing around 70 billion DNS requests). The results of these analyses provide customers with an enriched, qualified and reliable source of information.

DNS Security in Healthcare: The Gem in Your Cybersecurity Arsenal

The ransomware, malware and phishing attacks going on in the healthcare industry are quite alarming these days. The customers' data in the healthcare industry is more sensitive than in most industries, and this has proven to be a sweet spot for threat actors. Recent research by Infloblox reported that in 2022, there were over 546 major data breaches due to malicious activity. This follows a 4% increase over the 521 major data breaches reported by healthcare institutions in 2023.

Machine Learning in Security: Detect DNS Data Exfiltration Using Deep Learning

Since the Domain Name System (DNS) protocol is foundational for internet functionality, DNS traffic is allowed to move through firewalls without much scrutiny unlike HTTPS, FTP and SMTP. Malicious actors have successfully been able to exploit this advantage to transfer data between networks, which is beyond the original intention of DNS protocol.