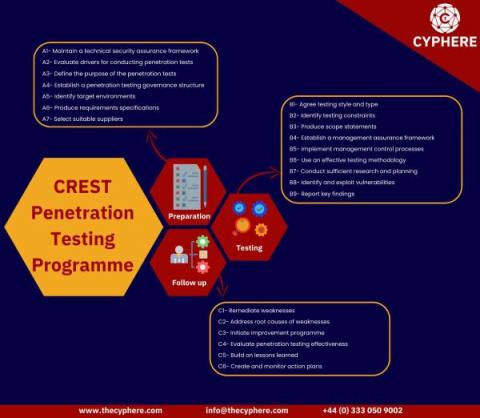
Penetration testing is an important component of the security strategy of any organisation. A well-conducted pen test can help IT teams ensure that their defences are up to par and are capable of protecting businesses and organisations against cyber security attacks.
“How does Detectify’s External Attack Surface Management platform compare to Penetration testing” or “What I’m really looking for is Penetration testing” are two statements we often hear when talking to prospects. We know that many of you are keen to understand how EASM compares with Penetration testing (Pen testing), so we’re exploring these two methodologies side-by-side.
PCI version 4.0 was released in March 2022, and all organizations that must be compliant with the regulation have a deadline of March 31, 2024 to do so. So, what does the new version say about pen testing? According to Requirement 11 of the Payment Card Industry Data Security Standard (PCI DSS), pen testing is required for organizations and entities that store, process, and/or transmit cardholder data.
Fortra’s Core Security recently released its 2023 Pen Testing Report, and there’s plenty to see. In this year’s report, IT decision-makers can learn what their peers are saying about why they pen test, how often they pen test, and whether or not they’re pen testing in-house, among other topics. Each year, Core Security collects and produces some of the industry’s most relevant data on the state of pen testing today.
The concept of Offensive Security is often misunderstood by clients who often confuse it with penetration testing, but these two solutions, while both vital, are in fact quite different. Offensive Security is a popular industry umbrella term for all things pertaining to an organization's strategy surrounding cybersecurity, whereas penetration testing is more singular involving security teams attempting to break into a client’s systems.
Penetration testing is a crucial part of a comprehensive cybersecurity plan. By simulating a real-world attack, a penetration test can help identify vulnerabilities and weaknesses across systems, networks, and applications before a malicious actor can exploit them. To get off on the right foot with a penetration test and get an accurate timeline and budget for the test, it’s important to have a proper scope. Learn how to scope a penetration test from the perspective of the Sedara Red Team.