Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Manufacturing Needs SASE: Securing Smart Factories and Global Operations

Imagine you’re the Director of IT for a global manufacturing company. You must keep production sites, suppliers, and remote workers securely connected while controlling costs and meeting compliance. Every day, new challenges arise: If this sounds familiar, you’re not alone. Manufacturing is rapidly evolving with Industry 4.0, where smart factories use automation, IoT, AI analytics, and real-time data to optimize production and efficiency.

SASE as a Journey: Why Single-Vendor Doesn't Mean Single Project

When IT leaders hear the term “single-vendor SASE,” many assume it implies an immediate, all-encompassing migration—a daunting project requiring the wholesale replacement of existing network and security infrastructure. This misconception can lead to hesitation in embracing a more modern and efficient approach to secure access. The reality, however, is quite different: SASE (Secure Access Service Edge) is a journey, not a single project.

Meeting Compliance Requirements with the Cato LAN NGFW

Simplify Compliance & Security with Cato’s Application-Aware LAN Firewall! In a distributed, cloud-first world, ensuring networking and security compliance is more challenging than ever. VLANs lack the granularity needed to enforce strict regulatory controls, and traditional firewall appliances add cost, complexity, and management overhead. What if you could extend your FWaaS to enforce microsegmentation inside the LAN?

Microsegmentation That Stops Lateral LAN Threat Movement with the Cato LAN NGFW

Stop Lateral Threat Movement with Cato’s LAN Next-Gen Firewall! Traditional VLAN-based segmentation is no longer enough to stop lateral movement within your corporate network. Attackers exploit east-west traffic, moving undetected between users, devices, and workloads. How do you enforce microsegmentation without increasing operational complexity? Cato Networks introduces L7 LAN NGFW, a native feature of the Cato SASE Cloud Platform that brings application-aware security to your local LAN. It prevents unauthorized access and restricts communication across VLANs without manual configurations or complex ACLs.

Protect Local Networks with Cato's Application-Aware LAN NGFW

Simplify LAN Security with Cato Networks’ LAN Next-Gen Firewall! Managing LAN security across multiple locations has always been a challenge—until now. Two common hurdles IT teams face: Hardware Hassles – Deploying, upgrading, and troubleshooting firewalls at each site is time-consuming and costly. Policy Complexity – Keeping rules clean and consistent across multiple locations can be a nightmare.

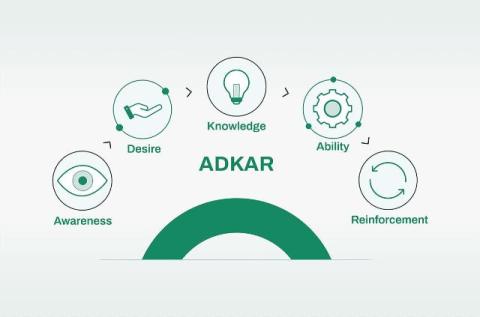
ADKAR: 5 stages to manage the human side of SASE change

Change isn’t optional—IT leaders know this better than anyone. IT has always been the backbone of the business, keeping everything secure, connected, and efficient. But the demands on IT—and the business—have changed. Cloud adoption, hybrid work, competitive pressures, and rising costs have exposed the cracks in legacy architectures and pushed them past their limits.