Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Governance on AWS: Discover, Observe, and Control AI in Production

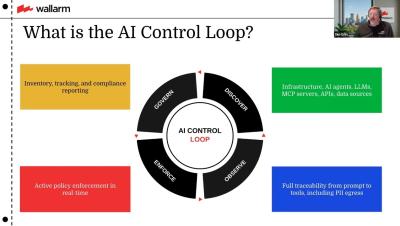
AI adoption within AWS environments is accelerating faster than most security and governance programs. AI agents, APIs, MCP servers, and model integrations are entering production across cloud environments, often without centralized visibility or runtime controls. In this webinar, you’ll see how teams can discover AI workloads across AWS accounts, understand what AI systems are actually doing at runtime, enforce policy in real time, and generate continuous governance evidence without slowing engineering teams down. The session focuses on practical operational capabilities for AI systems already running in production.
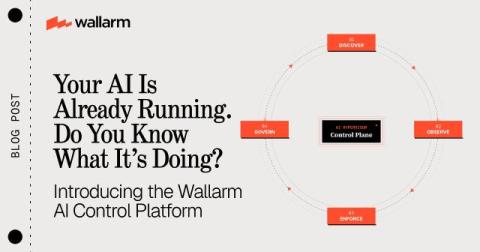
Introducing the Wallarm AI Control Platform: One closed loop for AI security and API security.

Every week, someone in your organization stands up an AI service. Maybe they told security about it, but probably not. By the time it shows up in your inventory, it has been running for weeks, processing data, calling external APIs, and doing things nobody formally reviewed.

New Security Gap: Your WAF Has No Idea What Your AI Is Doing

In this webcast, we get into why signature-based protection breaks down in AI-first environments, what behavioral detection and positive security models actually look like in production, and what it takes to evaluate whether your runtime tools are genuinely adapting to your environment or just adding noise to your stack.

What Your Board Gets Wrong About AI Security

Editor's note: This article was originally published by Craig Riddell on LinkedIn. It has been republished here with the author's permission. Boards are giving AI security more airtime than ever. What they're not giving is the right framing. A year or two ago, AI was mostly a question of experimentation risk. Today, it's tied directly to revenue, customer experience, operational efficiency, and competitive advantage. The urgency is real, and it's translating into aggressive deployment timelines.

Extending Security to MCP Servers: Closing a Critical Gap

The Model Context Protocol (MCP) is a de facto standard for providing structured access to privileged systems for AI agents and external integrations. It acts as a USB-C port for AI, enabling faster innovation by allowing organizations to expose tools, resources, and workflows without the time-consuming work of building APIs. Adoption has surged in recent months, and categories like payments, project management, and developer platforms are already beginning to reap the benefits.

6 Lessons Security Leaders Must Learn About AI and APIs

Most organizations treating AI security as a model problem are defending the wrong layer. Security teams filter prompts, patch jailbreaks, and tune model behavior, which is all necessary work, while the actual attack surface sits largely unexamined underneath. That surface is the API layer: the endpoints AI systems use to retrieve data, call tools, and take action on behalf of users. This isn't a theoretical gap.

Attacking the MCP Trust Boundary

Every secure API draws a line between code and data. HTTP separates headers from bodies. SQL has prepared statements. Even email distinguishes the envelope from the message. The Model Context Protocol (MCP), the fast-growing standard for connecting AI agents to external services, inherits that gap from the models it sits on top of.