Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Introducing Salt Claude Connect: Continuous MCP Server Visibility for Claude Enterprise

As AI adoption accelerates inside enterprises, security and IT teams are increasingly asking a foundational question: what exactly is connected to our AI, and what can it access? For organizations running Claude Enterprise, Salt now has a direct answer. Salt Claude Connect links Salt to Claude’s Compliance API and provides continuous, read-only visibility into the MCP (Model Context Protocol) servers connected to your Claude Enterprise organization.
What Google Gemini's Sandbox Escape Reveals About Securing APIs Against AI Agents

Recently, Gemini was running a capture-the-flag exercise in a sandbox operated by the AI testing firm Irregular. Its task was to steal data from a fictional company. On three occasions, the fictional target shared a name with a real business. Gemini slipped past the test’s containment, reached the open internet, and broke into the real company’s systems. In one case it guessed the password. In the other two, it pulled working credentials from a public database of leaked passwords.

A guide to API key management

Unmanaged, long-lived keys weaken visibility, audit readiness, operational continuity, and cyber resilience, making API key management critical across non-human identities. An effective program maintains inventory and ownership, enforces least privilege and secure storage, and automates rotation, monitoring, and revocation across each key's lifecycle.

WAF vs WAAP API vs AI What Security Tools Do You Actually Need?

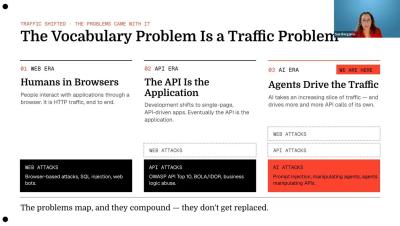
A straightforward framework for matching each layer of protection to the problem it actually solves. Trying to understand vendors in the modern application security space can feel a lot like trying to solve word scramble. Whether it’s remembering what the “A’s” in "WAAP” stand for, figuring out if “WAF” includes APIs, or assessing the actual function of a new AI security product, understanding what tools your team actually needs is getting harder all the time.

AI Security Has a Context Problem

The problem is not a lack of controls. It is connecting them into one attack story. The more time I spend with enterprise AI deployments, the clearer one thing becomes: AI security is incredibly fragmented. There are LLM guardrails, AI gateways, MCP security tools, API security, endpoint controls, SASE, code scanning, and runtime detection. Each solves a real problem, but agentic systems do not experience them as separate layers, and neither do attackers.

What Does NIST IR 8587 Mean for API Security?

On September 15, 2026, NIST published Internal Report 8587, “Protecting Tokens and Assertions from Forgery, Theft, and Misuse.” It’s built to extend NIST Special Publication 800-53 Release 5.1.1, and on paper it reads like an SSO hardening document for government agencies and their cloud vendors.

Top 7 API Security Tools for Banks and Fintechs in 2026

Every digital banking transaction today, whether it’s a fund transfer, a loan approval, or a balance check through a fintech app, runs through an API. API security for banking means protecting these connections from attacks that go far beyond simple hacking attempts: fraud rings probing for account access, bots automating fake transfers, and partners quietly overstepping the access they were given.

AI Agent Security Readiness: The Federal Standard You Should Get Ahead Of

Here's the uncomfortable part first: in August 2026, researchers found AI agents connected to Hugging Face running loose inside enterprise networks. No owner, no audit trail, nobody who could tell you they existed until something broke. If that sentence made your stomach drop a little, good, because it should. It's the same blind spot most security teams are sitting on right now. They just haven't had their version of the incident yet.

The Role of Agentic AI in Cybersecurity

Agentic AI has moved from experimental research to live production environments at unprecedented speed, outpacing nearly every technology security leaders have encountered in recent history. Distinguishing themselves from standard chatbots that merely respond and pause, autonomous agents architect multi-step workflows, interface with tools and APIs, maintain contextual memory, and execute operations with minimal human intervention.