Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The CISA Points Way Forward for More Effective Vulnerability Management with Directive 23-01

While tech sector media coverage on cybersecurity has primarily focused in recent years on trends such as ransomware attacks, vulnerabilities in the DevOps chain, and the growing role of AI in combating threats, a quiet but significant development has been advancing under the radar on several fronts: we refer to the more assertive stance taken by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) to elevate security best practices in government and the private sector.
The Long Tail of the Supply Chain: Leveraging Exposure Management to Mitigate Risk from Current or Former Vendors

Every organization must prioritize the security of its systems and the protection of its customers’ sensitive information, but exposure doesn’t only happen through applications your own team develops and controls. Incidents like the recent exposure of customer data by Juniper Networks serve as stark reminders of the challenges and risks associated with managing the exposure of software, hardware, and services that you use.

Effective Cybersecurity and Risk Management Starts Here

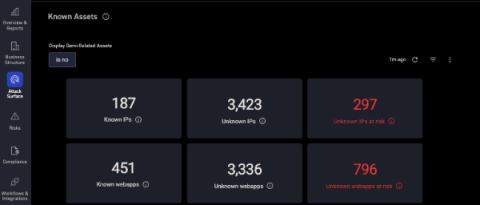
Hear first hand from Chief Technical Officer, Randy Watkins, as he explains why attack surface mapping is critical to an organization’s security posture and managing their IT assets. Learn how prioritizing security risk helps to cut through a sea of security issues and gives focus to security teams on what is critical.