Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Deconstructing the Agentic Stack: Why API Visibility Is the Ultimate Defense for AI Agents

AI agents do not create risk only when they hallucinate or produce an inaccurate answer. They create risk when they take the wrong action. A single user prompt can move through an application, reach an agent runtime, call a tool, trigger an MCP server, and touch a downstream API. By the time the action happens, the original request may be several layers away from the system that actually changes data, sends information, or executes a workflow. That is the problem security teams now face.
Salt Code

AI is writing more enterprise code than ever. The problem? AI coding assistants aren’t trained on your internal security policies, compliance requirements, or industry frameworks. The solution? Salt Code, the first agentic security solution to enforce security policies inside AI coding assistants. Salt Code brings policy-driven security to the moment code is created, helping developers generate compliant code by default from prompt to production.

Everyone Is Buying AI Guardrails. But Agents Have the Keys to the Car.

The first wave of AI security looked a lot like a WAF for LLMs: inspect the prompt, filter the output, block the obvious bad patterns. That was useful. It still is. But it was built for systems that mostly talked. Agents are different. They use tools, call APIs, access data, and change things. The confusion I keep seeing is simple: many teams think securing the model means securing the agent. It does not.

Salt Cloud Connect for Github

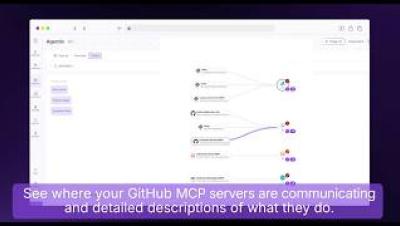
Your developers are shipping agents, MCP servers, and APIs faster than security can see them. GitHub Connect changes that. Salt scans your repositories and surfaces every agent, MCP server, and API hiding in your codebase, then maps them into the Agentic Security Graph. You see the agentic infrastructure forming in code, before it ever reaches production. No more waiting for runtime to find out what shipped. No more blind spots between dev and prod. Govern what's being built from day one.

Even Google says you cannot do AI security on one platform

This week, Connie Loizos, editor in chief of TechCrunch, sat down backstage with Francis de Souza, COO of Google Cloud, for a piece on the state of enterprise AI security. The interview is worth reading in full. Three points in it should reshape how every CISO is thinking about the next twelve months.

Salt Cloud Connect for Github

Your developers are shipping agents, MCP servers, and APIs faster than security can see them. GitHub Connect changes that. Salt scans your repositories and surfaces every agent, MCP server, and API hiding in your codebase, then maps them into the Agentic Security Graph. You see the agentic infrastructure forming in code, before it ever reaches production. No more waiting for runtime to find out what shipped. No more blind spots between dev and prod. Govern what's being built from day one.