Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Your AI Gateway Doesn't Solve This Security Problem #shorts #ai

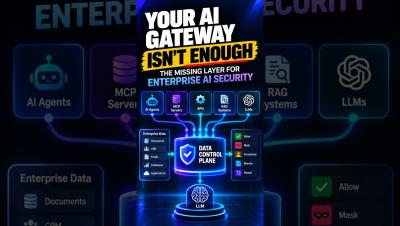
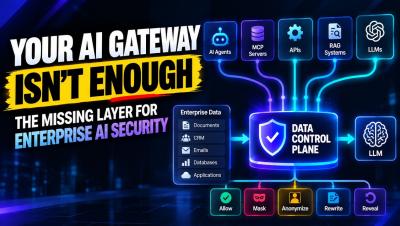
Your AI gateway doesn’t solve this. Neither does your identity platform. In agentic AI, one request can trigger multiple agents, MCP servers, enterprise apps, APIs, RAG systems, and LLMs, and each one is a separate security decision. The old question was “Can this user access this application?” The new question is “Can this task use this piece of enterprise data?”
Why AI Needs a Data Control Plane (Masking and Gateways Aren't Enough)

Your AI gateway and identity platform don’t decide whether a task can use a piece of enterprise data. In agentic AI, one request can trigger multiple agents, MCP servers, APIs, RAG systems, and LLMs, and each one is a separate security decision. This video explains why enterprise AI needs a runtime data control plane. It covers why identity alone can’t make the call, why masking PII isn’t enough when business context is sensitive, and how Protecto applies allow, mask, anonymize, rewrite, or selective reveal decisions across the AI workflow. It ends with a Fortune 100 multi-agent example.

Why Data Masking Breaks AI Workflows (And What Works Instead)

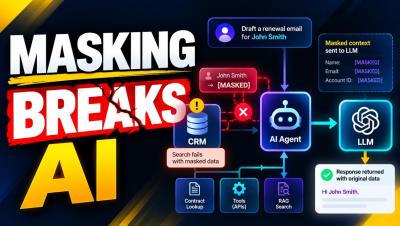
What if masking sensitive data actually broke your AI application? Most AI security strategies start with a simple rule: mask sensitive information before it reaches the LLM. But real AI workflows are more complex. An AI agent might need to search a CRM, retrieve a contract, check account details, call external tools, and generate a response. Each step may require a different level of access to sensitive data.

PDF Data Masking: The Missing Security Step in Document AI

PDF data masking is the security step most document AI stacks skip. Most companies building RAG pipelines, agentic workflows, or document intelligence systems have secured the model, the vector store, and the API. They haven’t secured the step before any of that: the data inside the document itself, before it enters the pipeline. That gap shows up everywhere documents meet AI.

Your AI Agents Need Data. But Should They See It? | LibreChat + Protecto

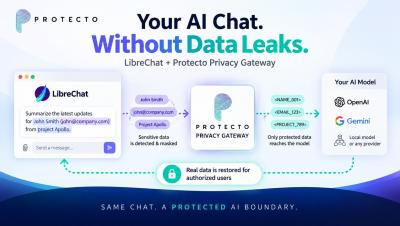
Can enterprises use powerful AI models with sensitive data without forcing everything into a self-hosted model? That's the problem this demo explores. In this session, we demonstrate Protecto Privacy Gateway integrated with LibreChat and show how sensitive enterprise data can be protected across AI chat, RAG, agents, MCP/tool calls, and long-running conversations.

How Protecto's Privacy Gateway protects data inside LibreChat

Self-hosting LibreChat gives you control over your chat infrastructure and conversation storage. But when you connect a hosted model such as OpenAI or Gemini, the prompts and context you send can still expose sensitive data. Protecto Privacy Gateway for AI Chat sits in that gap, in the request path between your LibreChat instance and whichever model you’ve connected.