Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Emerging Threat: (CVE-2026-70756) Oracle WebLogic Server Takeover via T3 and IIOP

CVE-2026-70756 is a vulnerability in the Core component of Oracle WebLogic Server, part of Oracle Fusion Middleware. An unauthenticated attacker with network access over the T3 or IIOP protocols can compromise the server and take full control of it. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical). Oracle rates it as easily exploitable, with no privileges and no user interaction required. Confidentiality, integrity, and availability impacts are all rated high.
Emerging Threat: (CVE-2026-76461) Cisco Secure Email Gateway Root RCE via Email Parsing

CVE-2026-76461 is a SQL injection vulnerability in the email parsing logic of Cisco AsyncOS Software for Cisco Secure Email Gateway, caused by insufficient validation of message content before it reaches a database query. An attacker who sends a crafted email message containing SQL statements can have those statements executed by the appliance as it processes the message. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical).

Introducing the CyCognito MCP Server: Full Exposure Context, On Demand

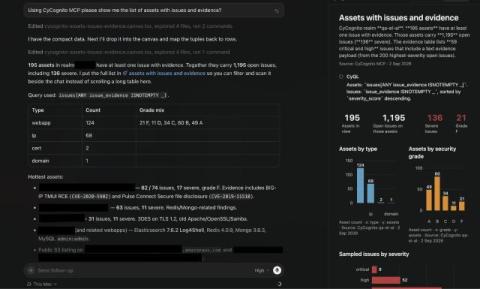
Today we are happy to announce the beta release of the CyCognito MCP server, which makes your external attack surface data consumable by any AI client that speaks the Model Context Protocol, including Claude, Cursor, and ChatGPT. The server runs on CyQL, the proprietary query language behind advanced search in our platform. CyQL is designed to ask precise questions about an attack surface, using operators suited to each type of asset, issue, and relationship.

Emerging Threat: (CVE-2026-78006) The Events Calendar Remote Code Execution via PHP Object Injection

CVE-2026-78006 is a deserialization of untrusted data vulnerability (CWE-502) in The Events Calendar, a WordPress plugin published by StellarWP, that allows an attacker to achieve remote code execution on the underlying host. The flaw sits in the is_safe_widget_instance function, whose guard against unsafe object data can be bypassed.

Emerging Threat: (CVE-2026-44756) SAP Remote Code Execution via Extended Passport Processing

CVE-2026-44756, tracked by SAP under the name OVERPASS, is a memory corruption vulnerability in the SAP kernel code that processes the Extended Passport (EPP), a standard SAP tracing structure used to follow call sequences across distributed system landscapes. The flaw stems from missing boundary validation during deserialization of EPP data, which causes unsafe memory behavior when the kernel processes externally supplied length fields. The vulnerability carries a CVSS v3.1 base score of 10.0 (Critical).

Emerging Threat: (CVE-2026-67281) MikroTik RouterOS Unauthenticated File Read via WebFig

CVE-2026-67281 is an unauthenticated file read vulnerability in WebFig, the web-based management interface in MikroTik RouterOS. A newly allocated session on the /jsproxy path retains a stale, uninitialized principal pointer that WebFig then uses for file authorization decisions. The vulnerability carries a CVSS v4.0 base score of 8.7 (High). A CVSS v3.1 base score has not been assigned in the CVE record at the time of writing.

Emerging Threat: (CVE-2026-81891) elFinder Remote Code Execution via ZIP Extraction MIME Bypass

CVE-2026-81891 is an unrestricted file upload vulnerability in Studio 42 elFinder, an open source web file manager embedded in a wide range of PHP applications and content management systems. The flaw sits in the checkExtractItems() function in php/elFinderVolumeDriver.class.php, which calls mimetypeInternalDetect() without passing the result through mimeTypeNormalize().